Skip to content

Toll Free / West Coast: (800) 700-7683 — East Coast: (800) 821-1782 — 9033 9th St. Rancho Cucamonga, CA 91730
DES Technologies
DES Technologies
  • IT Asset Disposition
    • Enterprise ITAD
    • Healthcare ITAD
    • Education Buyback
    • Government ITAD
    • Asset Recovery
    • ITAD Value Return
  • Data Security
    • Data Erasure
    • Physical Data Destruction
    • Degaussing
    • Phoenix Certified Erasure
    • Zero Trace Certified
    • Chain of Custody
    • NIST 800-88
  • Decommissioning & Asset Recovery
    • Decommissioning
    • Hardware Removal
    • Cloud Migration Services
    • On-Site ITAD, Data Destruction & Data Center Services
    • Secure Shipping
    • Media Labeling
  • Industries
    • Healthcare
    • Enterprise
    • Education
    • Government
    • Financial Services
    • International
  • Certifications
    • R2v3
    • ISO 9001:2015
    • ISO 14001:2015
    • ISO 45001:2018
    • Phoenix
    • HIPAA
  • Resources
    • Videos
    • Blog
    • Testimonials
    • Case Studies
    • ITAD Pricing Guide
    • How to Choose an ITAD Vendor
    • Certificate of Destruction Explained
    • About Us
    • Contact Us
    • Frequently Asked Questions
    • Privacy Policy
    • Warranty
    • Web Accessibility Statement
Menu
Contact Us
DES Technologies
  • IT Asset Disposition
    • Enterprise ITAD
    • Healthcare ITAD
    • Education Buyback
    • Government ITAD
    • Asset Recovery
    • ITAD Value Return
  • Data Security
    • Data Erasure
    • Physical Data Destruction
    • Degaussing
    • Phoenix Certified Erasure
    • Zero Trace Certified
    • Chain of Custody
    • NIST 800-88
  • Decommissioning & Asset Recovery
    • Decommissioning
    • Hardware Removal
    • Cloud Migration Services
    • On-Site ITAD, Data Destruction & Data Center Services
    • Secure Shipping
    • Media Labeling
  • Industries
    • Healthcare
    • Enterprise
    • Education
    • Government
    • Financial Services
    • International
  • Certifications
    • R2v3
    • ISO 9001:2015
    • ISO 14001:2015
    • ISO 45001:2018
    • Phoenix
    • HIPAA
  • Resources
    • Videos
    • Blog
    • Testimonials
    • Case Studies
    • ITAD Pricing Guide
    • How to Choose an ITAD Vendor
    • Certificate of Destruction Explained
    • About Us
    • Contact Us
    • Frequently Asked Questions
    • Privacy Policy
    • Warranty
    • Web Accessibility Statement
Contact Us
  • West Coast(800) 700-7683
  • East Coast(800) 821-1782
Linkedin-in Facebook-f X-twitter Youtube Instagram

Federal agencies faced one of their worst nightmares this past week when they were informed of a massive compromise by foreign hackers within their network management software. An emergency directive from the Cybersecurity and Infrastructure Security Agency (CISA) instructed all agencies using SolarWinds products to review their networks and disconnect or power down the company’s Orion software. 

Orion has been used by the government for years and the software operates at the heart of some crucial federal systems. SolarWinds has been supplying agencies for some-time as well, developing tools to understand how their servers were operating, and later branching into network and infrastructure monitoring. Orion is the structure binding all of those things together. According to a preliminary search of the Federal Procurement Data System – Next Generation (FPDS-NG), at least 32 federal agencies bought SolarWinds Orion software since 2006.

Listed below are some of the agencies and departments within the government that contracts for SolarWinds Orion products have been awarded to. Even though all them bought SolarWinds Orion products, that doesn’t mean they were using them between March and June, when the vulnerability was introduced during updates. Agencies that have ongoing contracts for SolarWinds Orion products include the Army, DOE, FLETC, ICE, IRS, and VA. SolarWinds estimates that less than 18,000 users installed products with the vulnerability during that time.
  • Bureaus of Land Management, Ocean Energy Management, and Safety and Environmental Enforcement, as well as the National Park Service and Office of Policy, Budget, and Administration within the Department of the Interior
  • Air Force, Army, Defense Logistics Agency, Defense Threat Reduction Agency, and Navy within the Department of Defense
  • Department of Energy
  • Departmental Administration and Farm Service Agency within the U.S. Department of Agriculture
  • Federal Acquisition Service within the General Services Administration
  • FBI within the Department of Justice
  • Federal Highway Administration and Immediate Office of the Secretary within the Department of Transportation
  • Federal Law Enforcement Training Center, Transportation Security Administration, Immigration and Customs Enforcement, and Office of Procurement Operations within the Department of Homeland Security
  • Food and Drug Administration, National Institutes of Health, and Office of the Assistant Secretary for Administration within the Department of Health and Human Services
  • IRS and Office of the Comptroller of the Currency within the Department of the Treasury
  • NASA
  • National Oceanic and Atmospheric Administration within the Department of Commerce
  • National Science Foundation
  • Peace Corps
  • State Department
  • Department of Veterans Affairs

YOU CAN READ THE JOINT STATEMENT BY THE FEDERAL BUREAU OF INVESTIGATION (FBI), THE CYBERSECURITY AND INFRASTRUCTURE SECURITY AGENCY (CISA), AND THE OFFICE OF THE DIRECTOR OF NATIONAL INTELLIGENCE (ODNI) HERE.

How the Attack was Discovered

When Cyber security firm FireEye Inc. discovered that it was the victim of a malicious cyber-attack, the company’s investigators began trying to figure out exactly how attackers got past its secured defenses. They quickly found out,  they were not the only victims of the attack. Investigators uncovered a weakness in a product made by one of its software providers, SolarWinds Corp. After looking through 50,000 lines of source code, they were able to conclude there was a backdoor within SolarWinds. FireEye contacted SolarWinds and law enforcement immediately after the backdoor vulnerability was found.

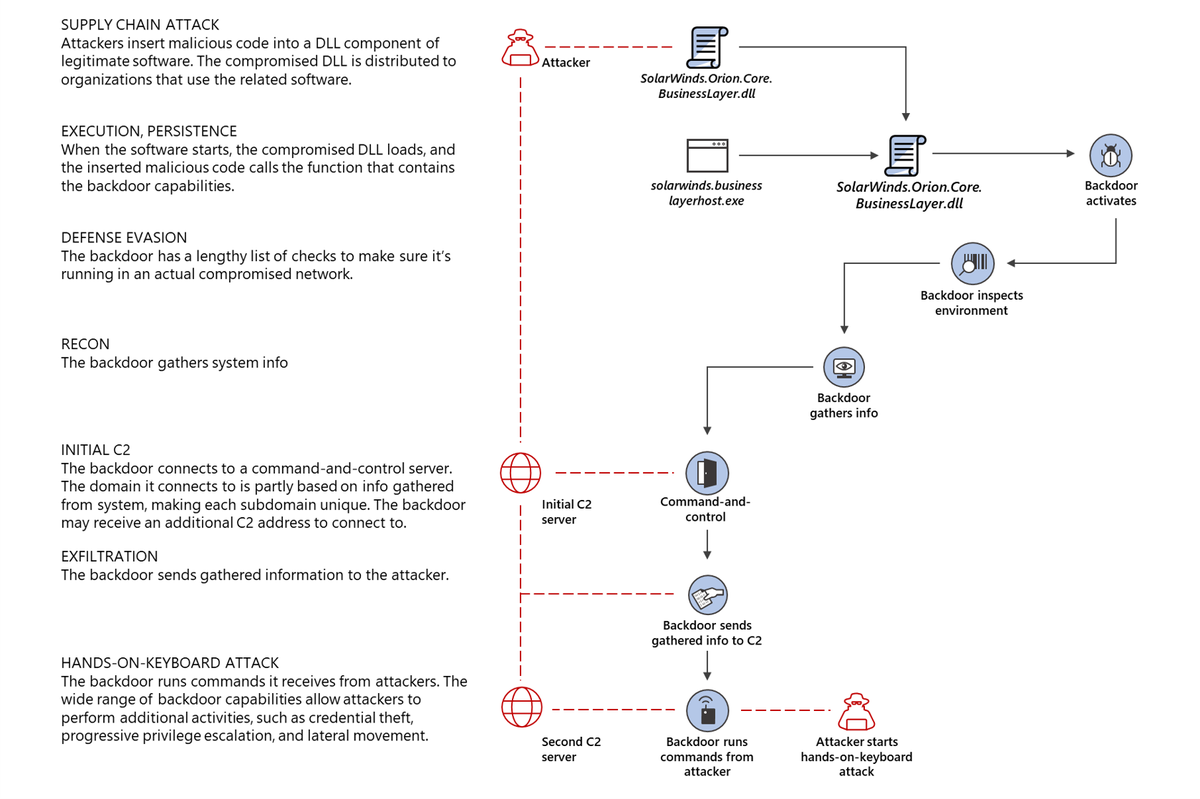
Hackers, believed to be part of an elite Russian group, took advantage of the vulnerability to insert malware, which found its way into the systems of SolarWinds customers with software updates. So far, as many as 18,000 entities may have downloaded the malware. The hackers who attacked FireEye stole sensitive tools that the company uses to find vulnerabilities in clients’ computer networks. The investigation by FireEye discovered that the hack on itself was part of a global campaign by a highly complex attacker that also targeted government, consulting, technology, telecom and extractive entities in North America, Europe, Asia, and the Middle East.

The hackers that implemented the attack were sophisticated unlike any seen before. They took innovative steps to conceal their actions, operating from servers based in the same city as an employee they were pretending to be. The hackers were able to breach U.S. government entities by first attacking the SolarWinds IT provider. By compromising the software used by government entities and corporations to monitor their network, hackers were able to gain a position into their network and dig deeper all while appearing as legitimate traffic.

Read how Microsoft and US Cyber Command joined forces to stop a vicious malware attack earlier this year.

How Can the Attack Be Stopped?

Technology firms are stopping some of the hackers’ key infrastructure as the U.S. government works to control a hacking campaign that relies on software in technology from SolarWinds. FireEye is working with Microsoft and the domain registrar GoDaddy to take over one of the domains that attackers had used to send malicious code to its victims. The move is not a cure-all for stopping the cyber-attack, but it should help stem the surge of victims, which includes the departments of Treasury and Homeland Security.


According to FireEye, the seized domain, known as a “killswitch,” will affect new and previous infections of the malicious code coming from that particular domain. Depending on the IP address returned under certain conditions, the malware would terminate itself and prevent further execution. The “killswitch” will make it harder for the attackers to use the malware that they have already deployed. Although, FireEye warned that hackers still have other ways of keeping access to networks. With the sample of invasions FireEye has seen, the hacker moved quickly to establish additional persistent mechanisms to access to victim networks.


The FBI is investigating the compromise of SolarWinds’ software updates, which was linked with a Russian intelligence service. SolarWinds’ software is used throughout Fortune 500 companies, and in critical sectors such as electricity. The “killswitch” action highlights the power that major technology companies have to throw up roadblocks to well-resourced hackers. This is very similar to Microsoft teaming up with the US Cyber Command to disrupt a powerful Trickbot botnet in October.

Join Our

Newsletter

Join our newsletter for helpful tips, company news, special offers, and updates delivered straight to your inbox.
No spam, just useful content.

  • Sorry, this service is unavailable in your country.

  • Should be Empty:

Secure Enterprise IT Asset Disposition & Data Destruction Solutions You Can Trust.

R2v3 certified and NIST-compliant
ITAD services for regulated industries
nationwide since 1965.

Services

  • ITAD
  • Secure Data Destruction
  • Asset Recovery & Remarketing
  • Data Center Decommissioning
  • On-Site ITAD, Data Destruction & Data Center Services
  • Secure Chain of Custody
  • ITAD
  • Secure Data Destruction
  • Asset Recovery & Remarketing
  • Data Center Decommissioning
  • On-Site ITAD, Data Destruction & Data Center Services
  • Secure Chain of Custody

Industries

  • Healthcare
  • Government
  • Enterprise
  • Financial Services
  • Education
  • International
  • Healthcare
  • Government
  • Enterprise
  • Financial Services
  • Education
  • International

Compliance

  • R2v3 Certification
  • NIST 800-88 Compliance
  • Phoenix Certified
  • Zero Trace Certified
  • Chain of Custody
  • Shipping & Tracking
  • R2v3 Certification
  • NIST 800-88 Compliance
  • Phoenix Certified
  • Zero Trace Certified
  • Chain of Custody
  • Shipping & Tracking

Contact

  • DES Technologies
    9033 9th St.
    Rancho Cucamonga, CA 91730
  • +1 (800) 700-7683
  • Monday - Friday:
    9:00AM - 5:00PM PT
REQUEST EVALUATION

Privacy Policy. Web Accessibility Statement. Warranty Guarantee.

© 2026 DES Technologies. All Rights Reserved.
Website created with 💛 by mrrssy.

Certified ITAD. Secure Data Destruction. Asset Recovery. Nationwide.

X-twitter Facebook Linkedin Youtube Instagram
Accessibility Adjustments

Powered by OneTap

How long do you want to hide the toolbar?
Hide Toolbar Duration
Select your accessibility profile
Vision Impaired Mode
Enhances website's visuals
Seizure Safe Profile
Clear flashes & reduces color
ADHD Friendly Mode
Focused browsing, distraction-free
Blindness Mode
Reduces distractions, improves focus
Epilepsy Safe Mode
Dims colors and stops blinking
Content Modules
Font Size

Default

Line Height

Default

Color Modules
Orientation Modules

We use cookies to provide you with the best browsing experience, personalize content of our site, analyse its traffic and show you relevant ads. See our privacy policy for more information.


Powered by WP Full Picture

Statistics

I want to help you make this site better so I will provide you with data about my use of this site.

Personalisation

I want to have the best experience on this site so I agree to saving my choices, recommending things I may like and modifying the site to my liking

Marketing

I want to see ads with your offers, coupons and exclusive deals rather than random ads from other advertisers.

Powered by WP Full Picture

What are you looking for

SEARCH Our Site

Get In Touch

CONTACT US